
ClassNK endorsed a useful inventory tool on November 5, 2026. It did not certify a compliant ship. Anyone treating the announcement as proof of IACS compliance is reading the headline and skipping the scope disclaimer, and the disclaimer is the whole story.
CYTUR-SBOM is a platform that inventories shipboard hardware, software, and firmware, maps assets to CPE and CVE records, and logs assessment evidence. For shipyards navigating IACS UR E26 and E27 on newbuilds, that is welcome validation of structured cyber evidence. A clean inventory is genuinely hard to build across a vessel’s computer-based systems. It is also only the first step, and ClassNK said so in the announcement itself.
Read the scope disclaimer first
ClassNK granted its Innovation Endorsement for Products and Solutions to CYTUR-SBOM on November 5, 2026. The release states plainly that the endorsement does not cover Chapters 4 and 5 of Part X of the ClassNK Rules for the Survey and Construction of Steel Ships, nor IACS Unified Requirements UR E26 Rev.1 and E27 Rev.1. That sentence is not boilerplate. It draws the line between an innovative product and a compliant vessel.
CYTUR also announced RINA Novel Technology Approval for the same platform on October 28, 2026. That is a second, separate recognition from a second classification society. Nothing in either announcement certifies IACS E26 or E27 compliance, and neither society’s recognition should be presented as if it does.
An inventory is not a compliance program. It is the raw material one is built from.
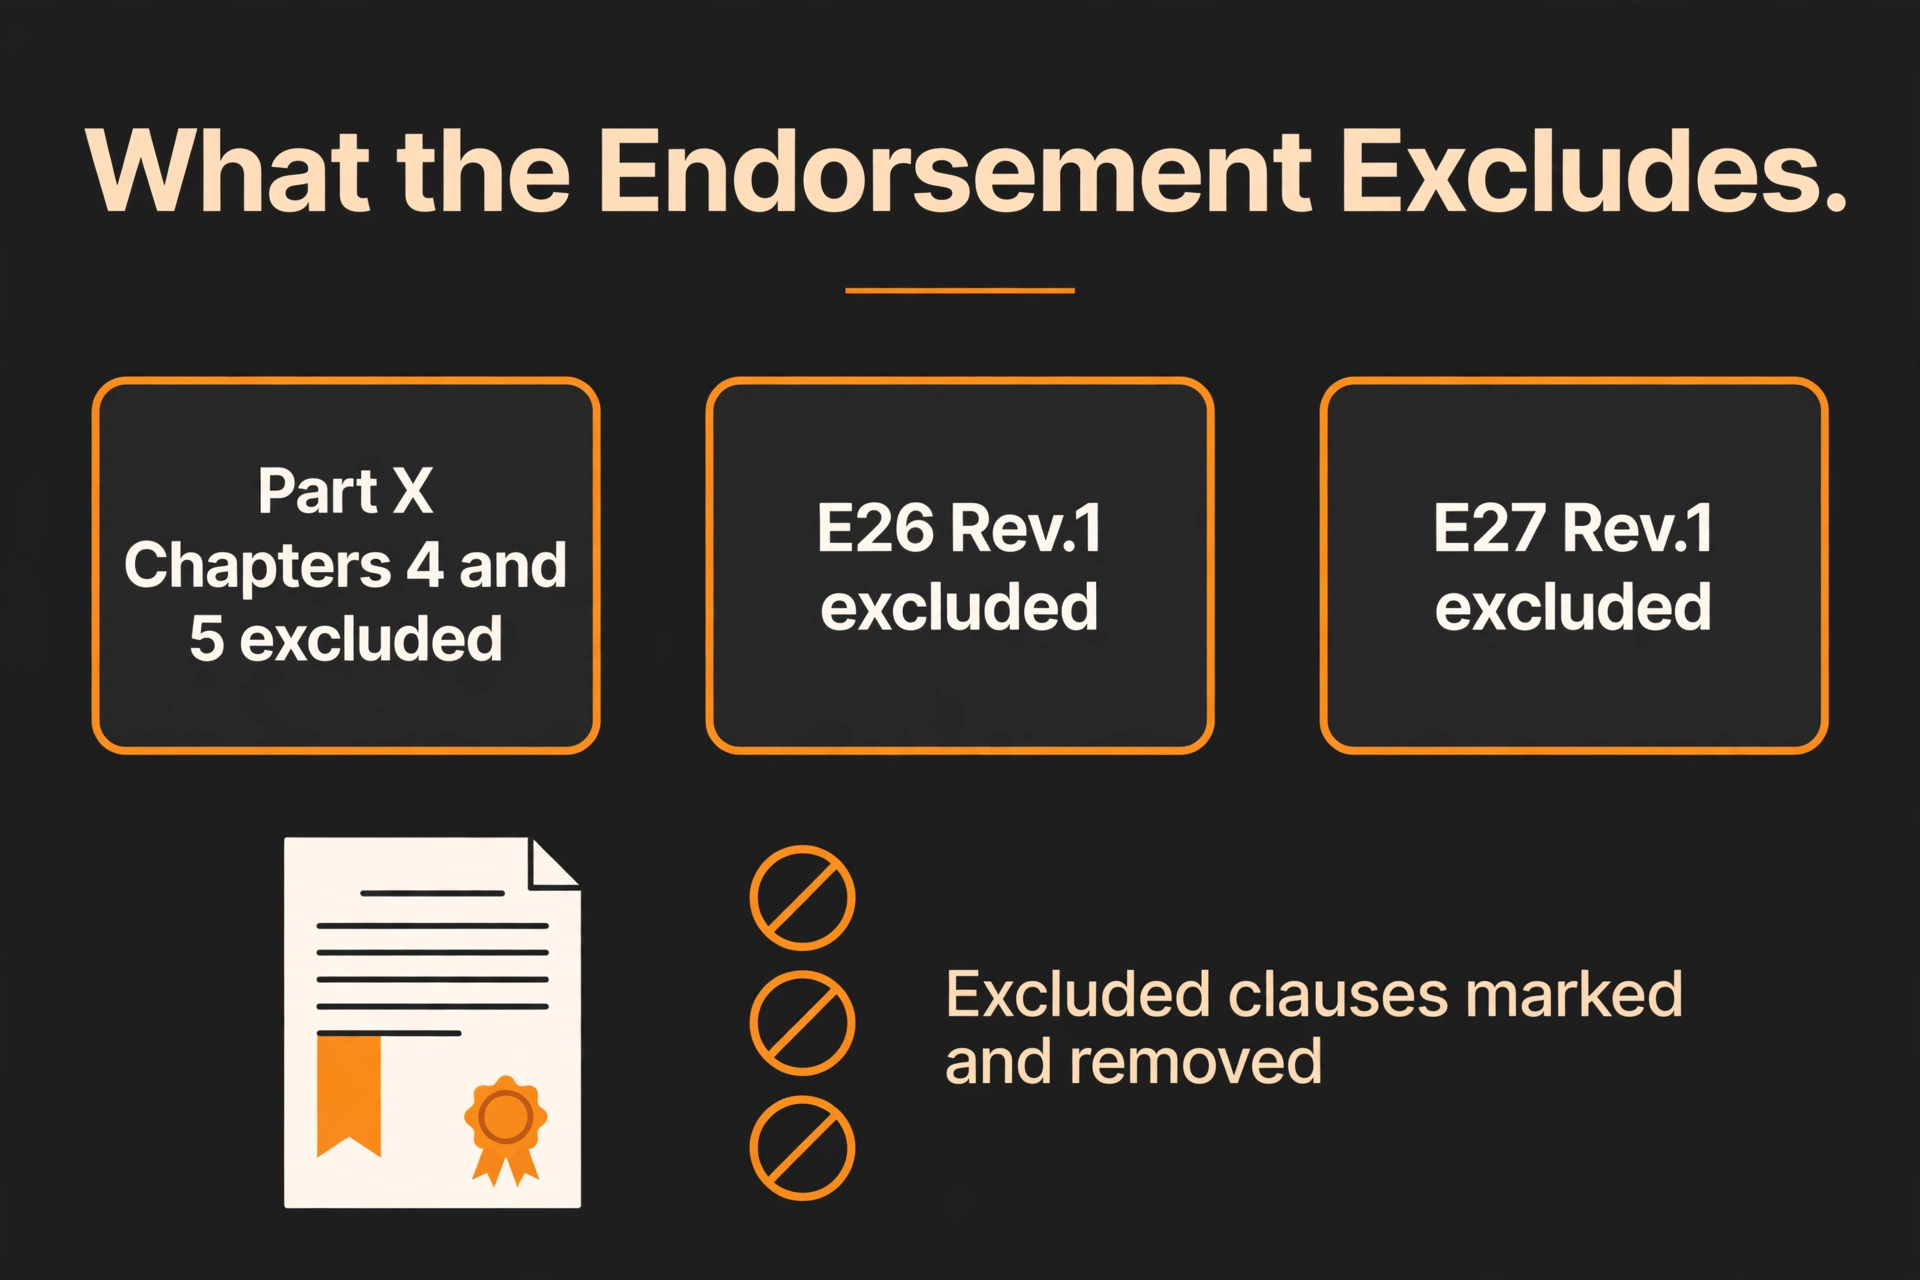
ClassNK press release, Nov 5, 2026. The exclusion is in the announcement itself.
What E26 and E27 actually require
IACS UR E26 covers vessel-level cyber resilience across design, commissioning, and operation. UR E27 covers supplier-level security capabilities for onboard computer-based systems. Both apply in Rev.1 to vessels contracted for construction on or after July 1, 2024. Class societies and owners require evidence that an inventory alone cannot provide.
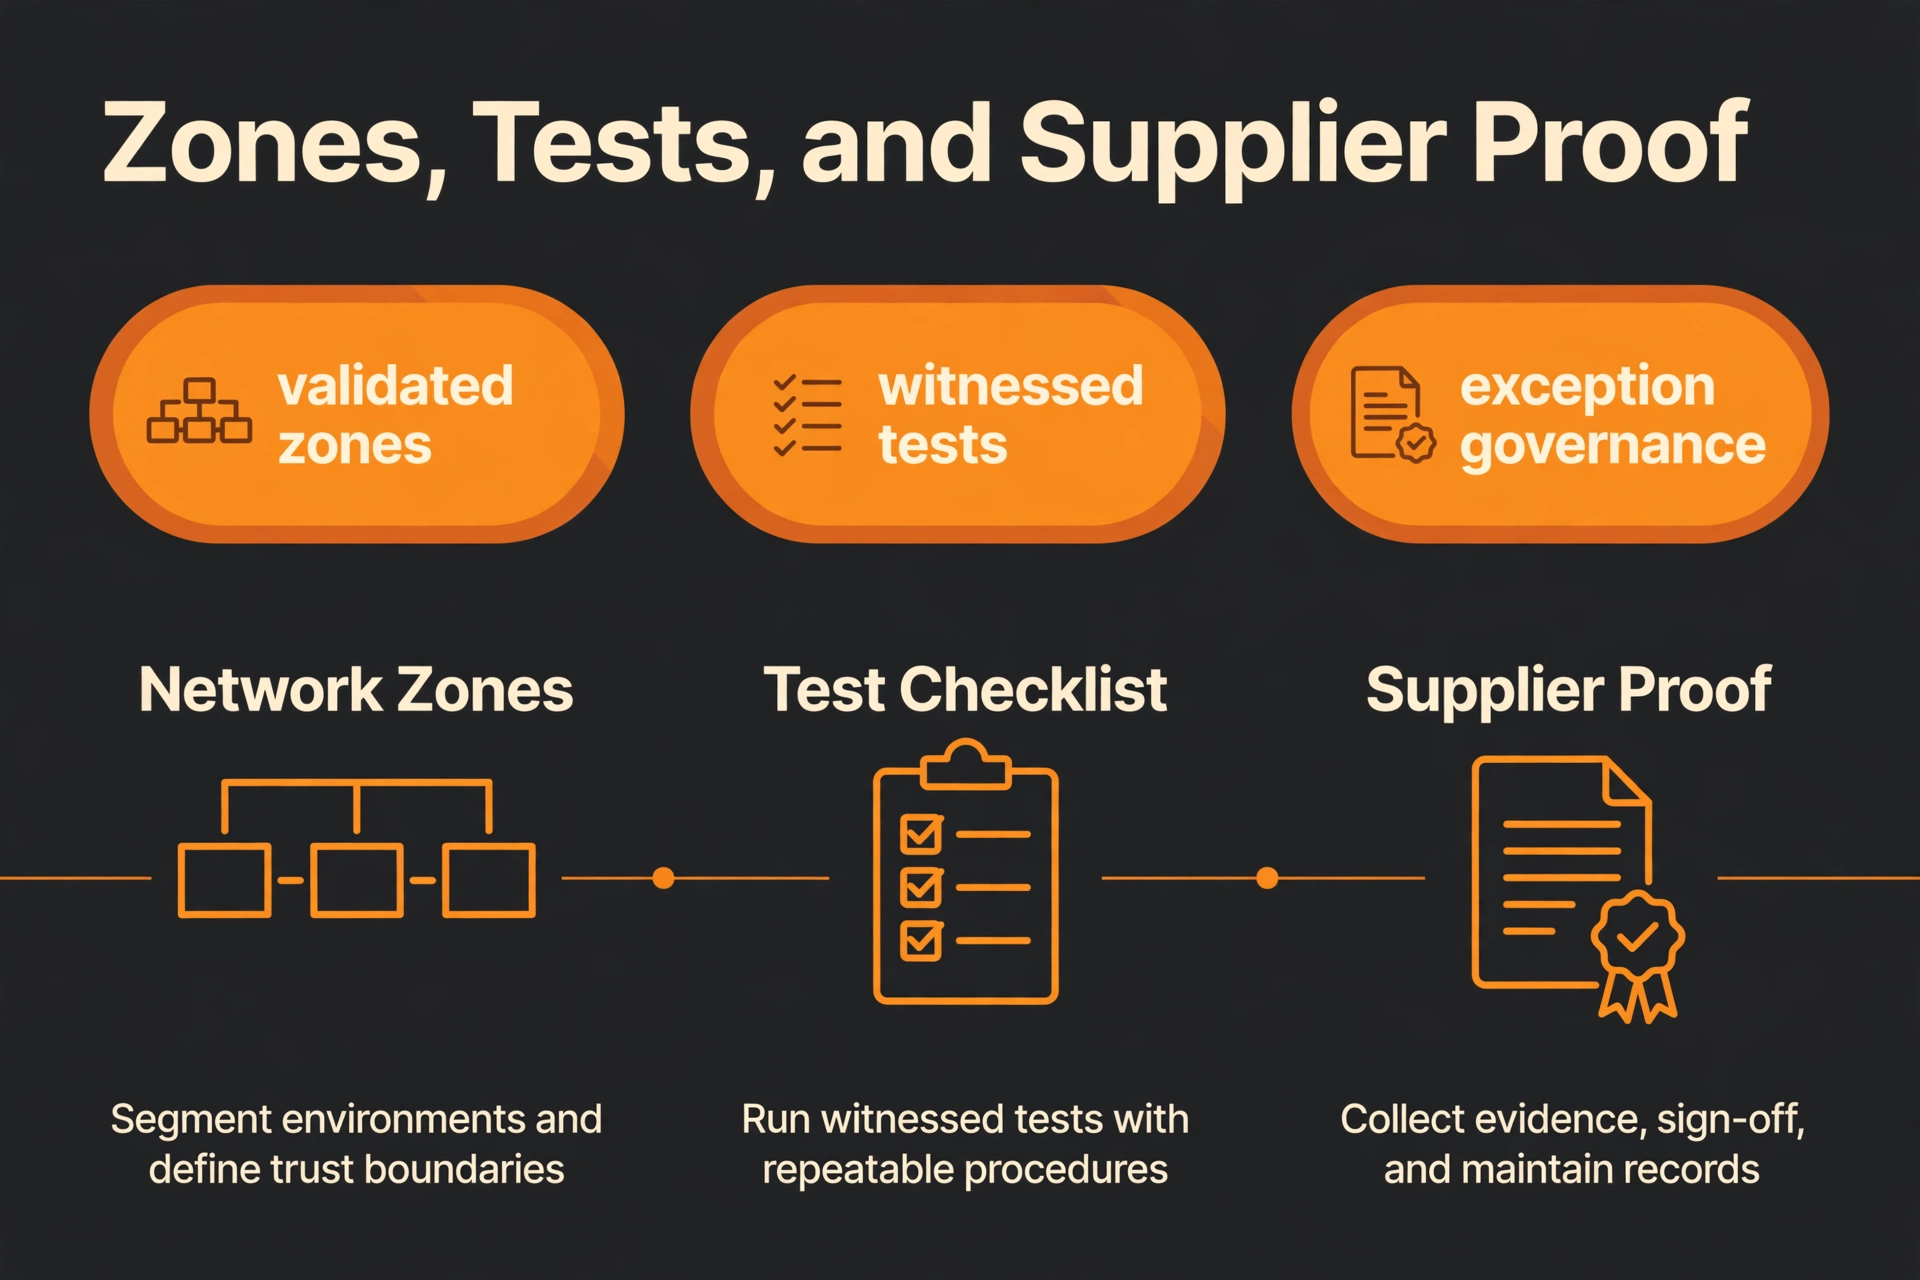
IACS UR E26 and E27 Rev.1 requirements for newbuilds contracted on or after July 1, 2024.
| Requirement | What an SBOM inventory proves | What is still needed |
|---|---|---|
| Validated security zones and segmentation | Which components exist and where they sit | Zone boundaries tested, with controlled change management |
| Commissioning cyber-resilience tests | Which vulnerabilities are listed against each asset | Test procedures run and witnessed, with evidence kept |
| Supplier security capability | Which supplier products are installed | Type-approval documentation and vulnerability-handling commitments |
| Exception governance | Which CVEs remain open | Each exception dispositioned, owned, and time-bound |
A CVE list tells an owner what is vulnerable. It does not tell an owner whether the vulnerable component sits behind a validated zone boundary, whether the commissioning test actually ran, whether the supplier will patch it, or whether anyone accepted the residual risk in writing. Those are the questions a surveyor asks, and an inventory answers none of them.
Suppliers and ports are now part of the drill
Two early-November developments show how fast the assurance boundary is expanding beyond the vessel itself. On November 3, 2026, Korea’s Internet and Security Agency ran a joint maritime cybersecurity drill at BEXCO in Busan with five shipping and ship-management firms, the Korea Coast Guard, the Korea Shipowners’ Association, and the Korea Ship Managers’ Industry Association. The scenario combined fraudulent port-authority emails with a corrupted shipboard software update from a compromised supplier workstation, disrupting ship-to-shore communications. The drill ran through four stages of incident response, including supply-chain attack handling. This was a scenario, not an incident. No vessel was actually attacked. The point of the exercise is that a supplier workstation is now a plausible path to the ship, and the drill treated it as one.
On November 5, 2026, UNCTAD TrainForTrade and IAPH launched a port cybersecurity awareness game at the IAPH World Ports Conference in London. Twenty-five port experts played scenarios covering software and smartphones, automation and charging stations, IoT and 5G, and building a cybersecurity team. The game is built on IAPH’s Cyber Resilience Guidelines for Emerging Technologies. The game is training, not an incident. It signals that ports, shore charging, and electrified terminal equipment now sit inside the assurance boundary, and that the people who run them are being trained as part of it.
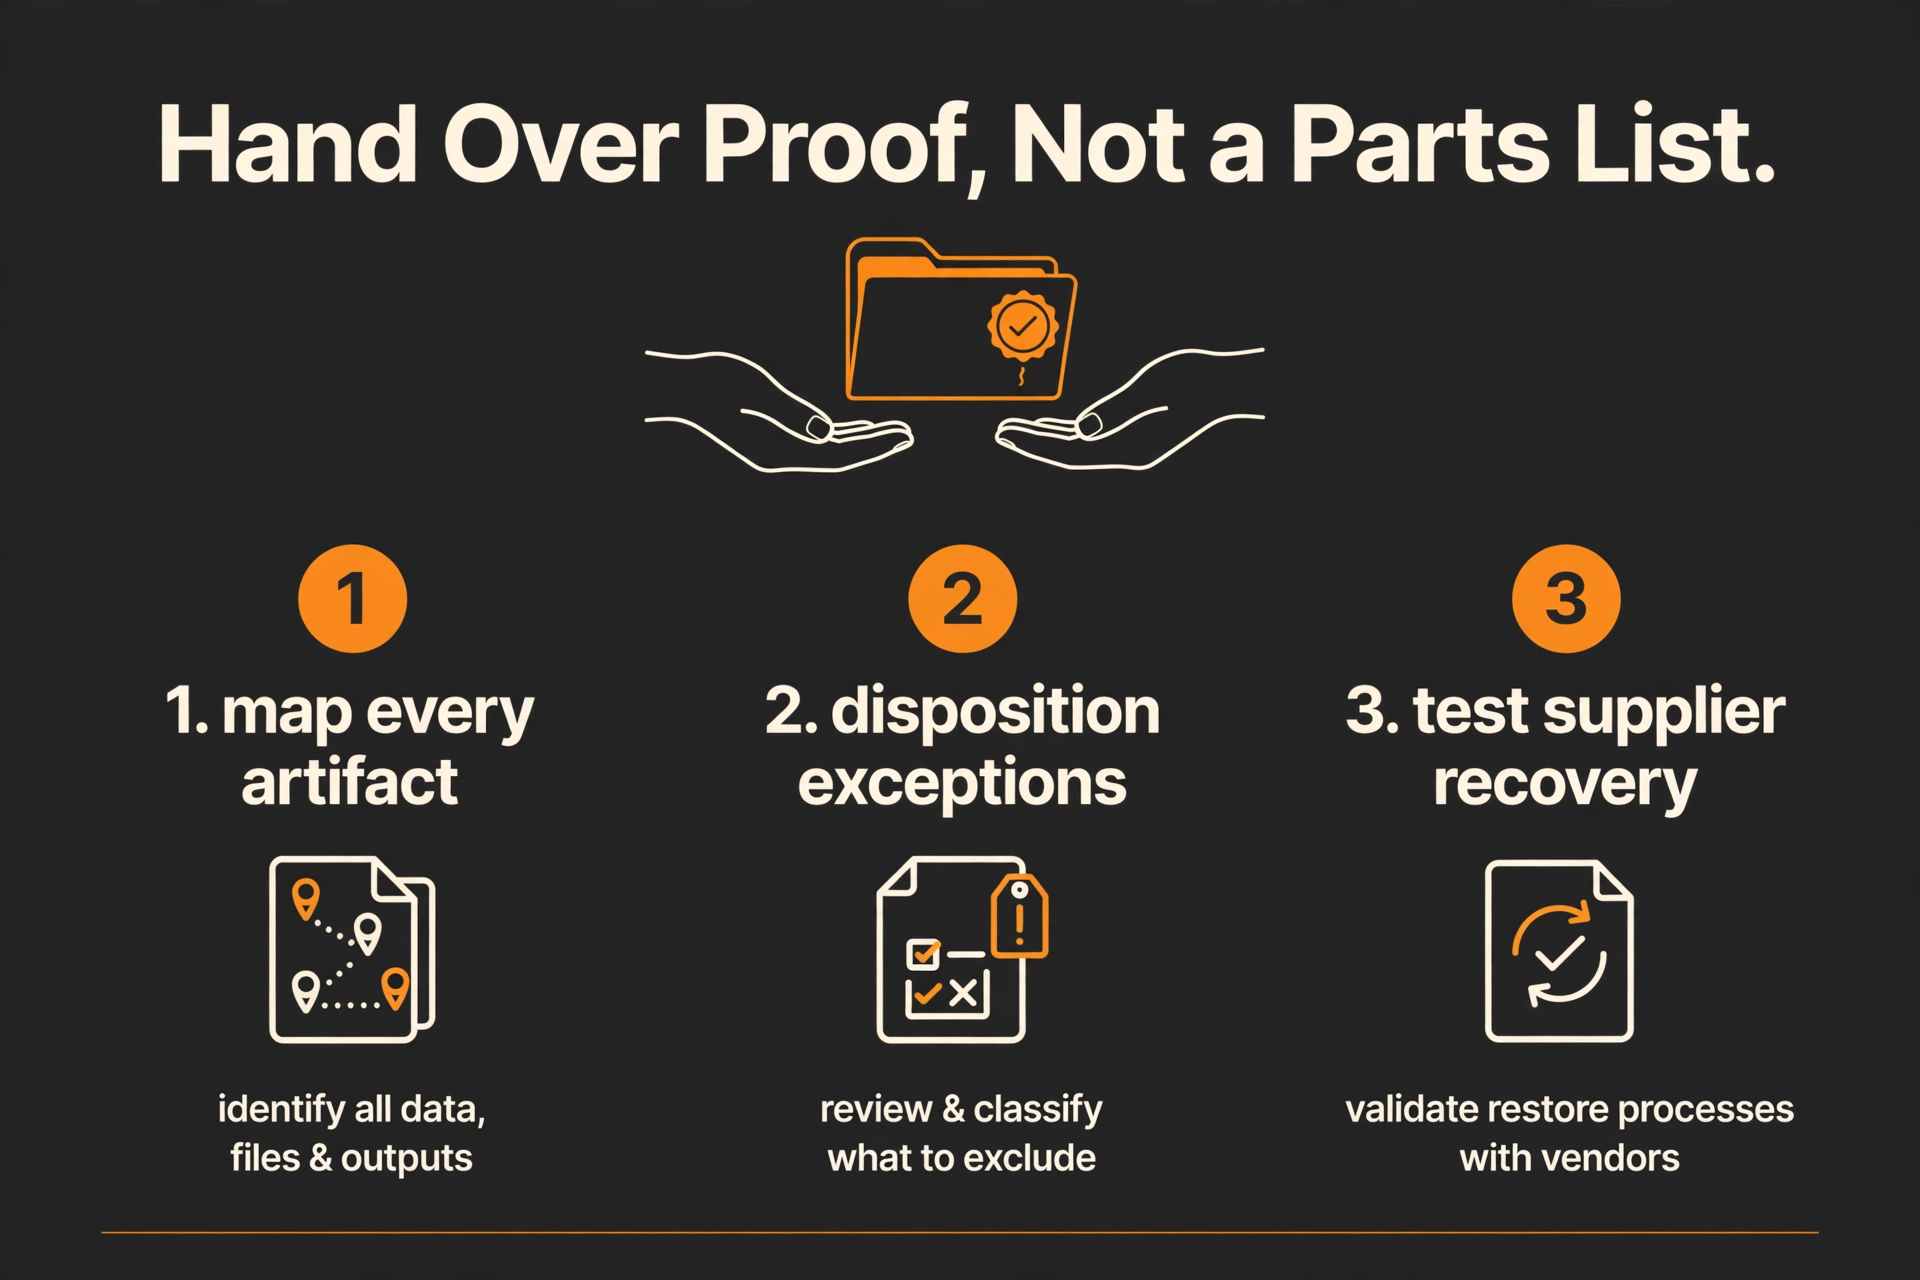
CSI Builder-to-Operator Cyber Handover Pack, mapped to IACS E26/E27 and USCG 33 CFR Part 101, Subpart F.
What to do before July 16, 2027
U.S.-flagged vessels, MTSA facilities, and OCS facilities face the July 16, 2027 USCG deadline for Cyber Security Officer designation, Cybersecurity Assessments, and Cybersecurity Plans under 33 CFR Part 101, Subpart F. Initial personnel training already came due on January 12, 2026. The Coast Guard published NVIC 02-26 guidance with templates on October 22, 2026. The runway is now measured in months, not years.
Builders and operators should stop treating scanning tools as compliance programs. Package the SBOM and CVE outputs inside a Builder-to-Operator Cyber Handover Pack. Map every artifact to the IACS E26 and E27 requirement it supports and to the corresponding USCG requirement. Disposition every open exception with an owner and a date. Test supplier-update recovery before vessel delivery, the exact failure the KISA drill rehearsed, so the first corrupted update does not arrive as a surprise. A handover pack that survives a surveyor’s questions is the difference between an inventory and a program.
Pelorus is built for that handover. Its Maritime Assurance Layer unifies asset and SBOM inventories with requirement-mapped evidence, supplier-update provenance, and ship-to-shore response exercises, so a vessel clears both class and Coast Guard scrutiny without last-minute delays. The endorsement of a good tool changes nothing about that work. It only makes the raw material easier to gather.
Sources
- ClassNK. “ClassNK grants Innovation Endorsement for Products & Solutions to CYTUR-SBOM developed by CYTUR.” Nov 5, 2026. https://www.classnk.or.jp/hp/en/news.aspx?id=15862&layout=1&type=p
- Safety4SEA. “South Korea conducts joint maritime cybersecurity response drill.” Nov 5, 2026. https://safety4sea.com/south-korea-conducts-joint-maritime-cybersecurity-response-drill/
- IAPH. “IAPH2026: cybersecurity game makes conference debut.” Nov 16, 2026. https://www.iaphworldports.org/news/iaphnews/23287/
- UNCTAD TrainForTrade. “New game on cybersecurity awareness in ports.” Nov 5, 2026. https://tft.unctad.org/en/2026/11/05/new-game-on-cybersecurity-awareness-in-ports/
- U.S. Coast Guard. Cybersecurity in the Marine Transportation System, 33 CFR Part 101, Subpart F.



