
 EDR comparison hub
Warden vs. traditional security. See the difference that matters.
Every EDR comparison here asks the same question of each vendor: what state does an unknown file hold while the verdict is still forming, and who has to act on it?
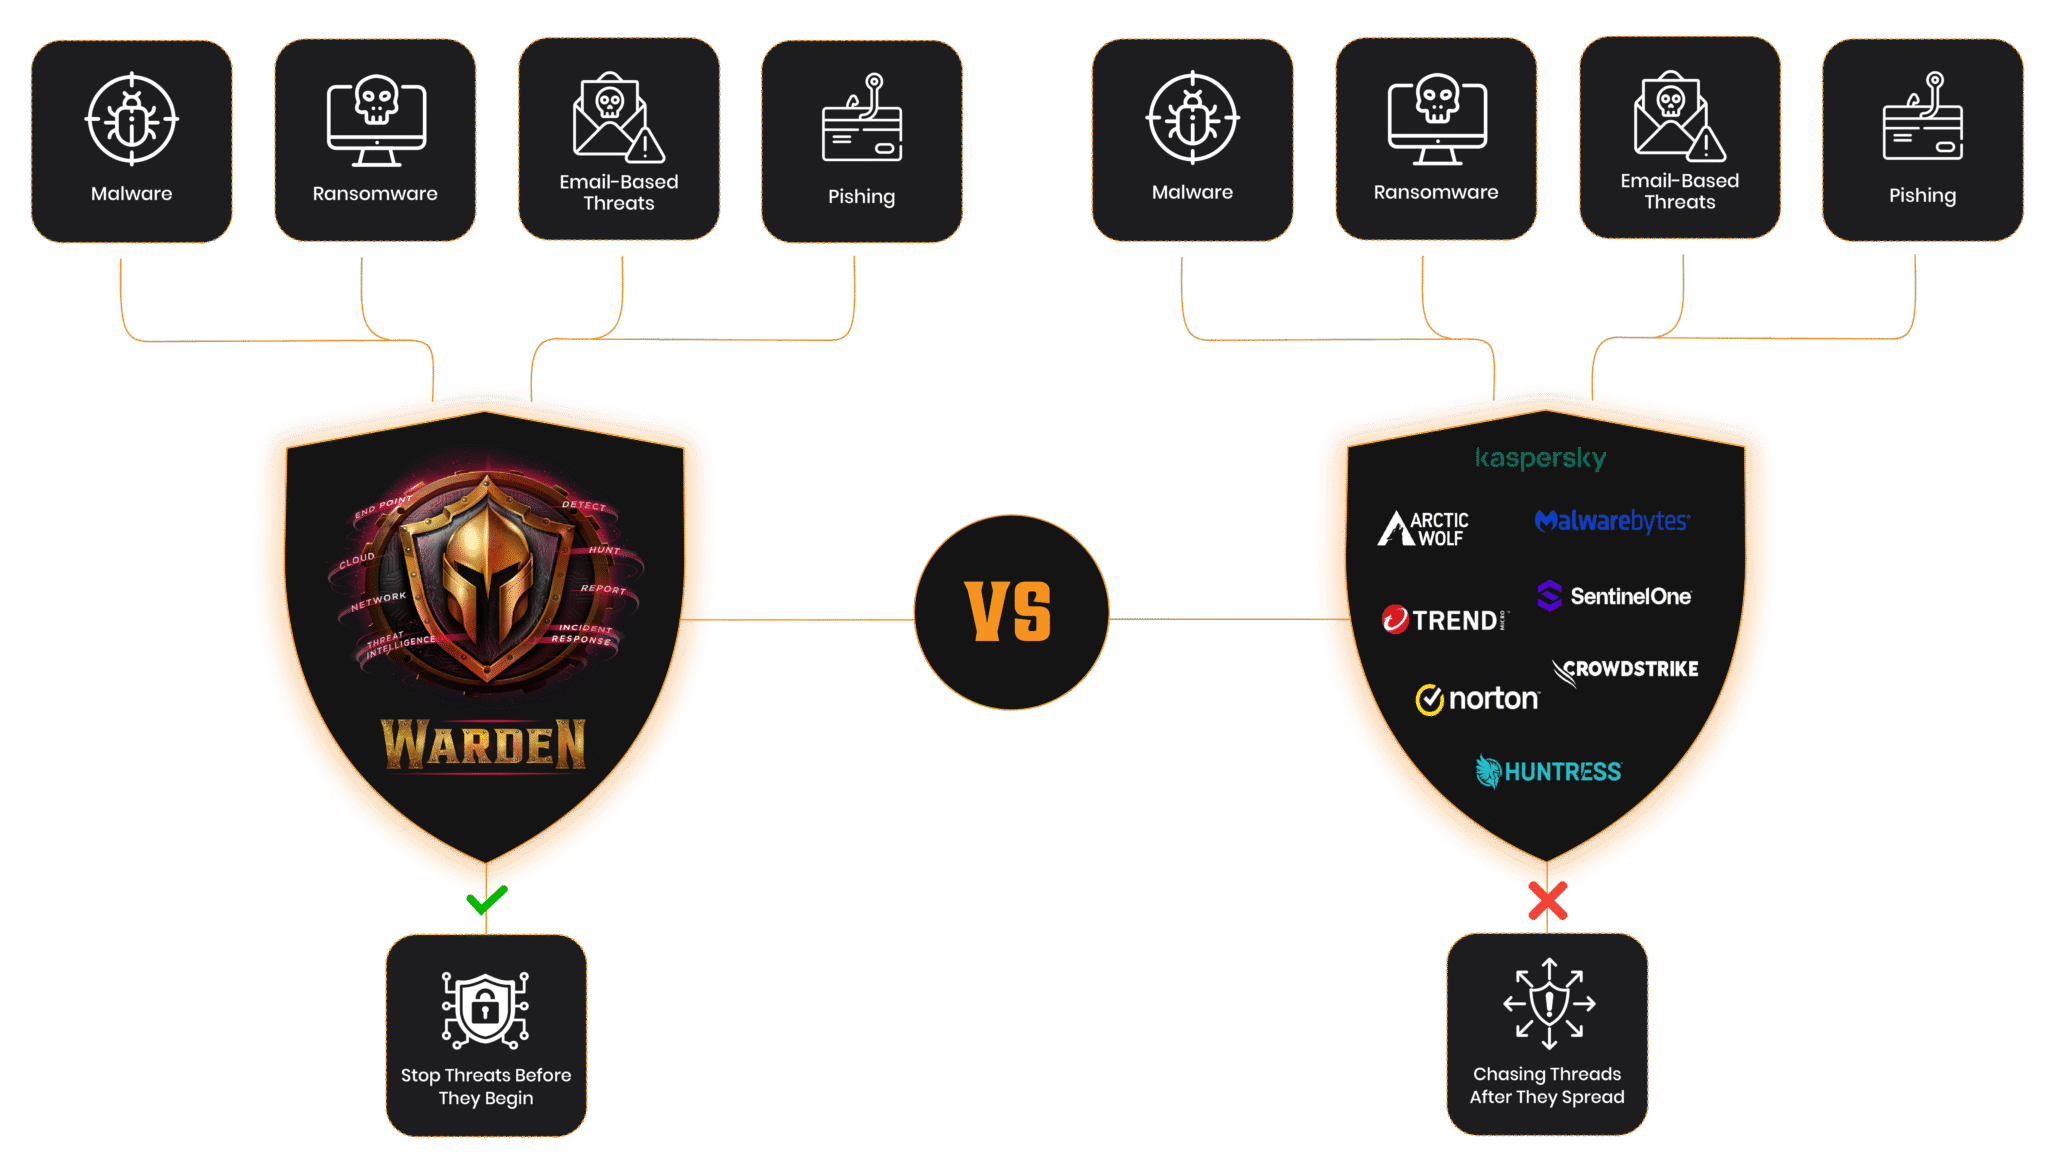
Warden contains unknowns before they run with full access. Detection-based platforms let them run and intervene once behavior looks malicious. Both can stop threats. Each comparison shows where the difference matters for your team.

Published weekly from Xcitium Threat Labs data. Latest period: 14 Sep - 20 Sep 2026.
Three pages per vendor, one for each stage of the decision.
Start with the page that matches the question you are answering now. Each one links to the other two.
Head-to-head
For teams evaluating Warden against one named vendor. Covers the architectural difference, a ten-dimension comparison table, what each package includes, cost, and running both during a pilot.
Answers: which architecture stops this, and what does it cost to run?
Alternatives
For teams reconsidering their current vendor and building a shortlist. Lists the credible alternatives, when each one fits, and where Warden does and does not belong.
Answers: what else should I be looking at?
Migration guide
For teams that have decided to move. Covers the managed EDR model, what your team still owns after the switch, the rollout sequence, and a cost model you set to your own endpoint count.
Answers: how do we switch without a gap in coverage?
Why Warden is different
Learn how detection tools fail over time
Traditional detection tools often look effective at first, but over time attackers bypass alerts, gain deeper access, and escalate the breach. The longer the gap, the bigger the risk.
Hours
Initial alerts generated but most threats slip past undetected.
Days
Missed detection allows attacker foothold and lateral movement.
Weeks
Traditional tools fail completely as the breach escalates.

Pick your current vendor.
Fourteen vendors, grouped by how they decide what to stop. Filter by approach, then open the page that matches where you are in the decision.
CrowdStrike Falcon
Microsoft Defender
SentinelOne
Sophos
Bitdefender
Malwarebytes
Symantec
Trend Micro
Trellix
Check Point
Kaspersky
Huntress
Arctic Wolf
ThreatLocker
Vendor claims on each page cite dated public documentation and pricing.
EDR comparison FAQ
What does this EDR comparison measure?
+
Each page compares how a platform treats an unknown file before a verdict exists, who has to act when something is flagged, what the package includes, and the fully loaded cost to run it. Vendor claims are drawn from dated public documentation and pricing.
How is Warden different from detection-based EDR?
+
Detection-based EDR lets unknown code run and intervenes once its behavior looks malicious. Warden runs unknown code inside containment from the first instruction, so it cannot reach the file system, registry or network with full access while it is being analyzed.
Can Warden run alongside my current EDR during a pilot?
+
Yes. Warden is designed to run next to an existing endpoint agent, so you can compare both on the same endpoints before deciding. Each migration guide lists the coexistence steps for that vendor.
Where does the Warden performance record come from?
+
The weekly record is published on the Cyber Weekly Insights page from Xcitium Threat Labs data statistics. It reports device and file states each week, including whether any contained activity reached operational impact.
Which page should I read first?
+
Read the head-to-head page if you are comparing Warden with one named vendor, the alternatives page if you are building a shortlist, and the migration guide if you have already decided to switch.
The only containment-first protection
Every comparison on this page asks what state an unknown file holds while its verdict forms. A side-by-side pilot answers that on your own endpoints, running next to the tool you use today, with no rip-and-replace.