
When the Gateway Fails, What Stops the Action?
The LiteLLM vulnerability (CVE-2026-59822) makes the question concrete: if your gateway accepts a forged identity, what still prevents the action? At a […]
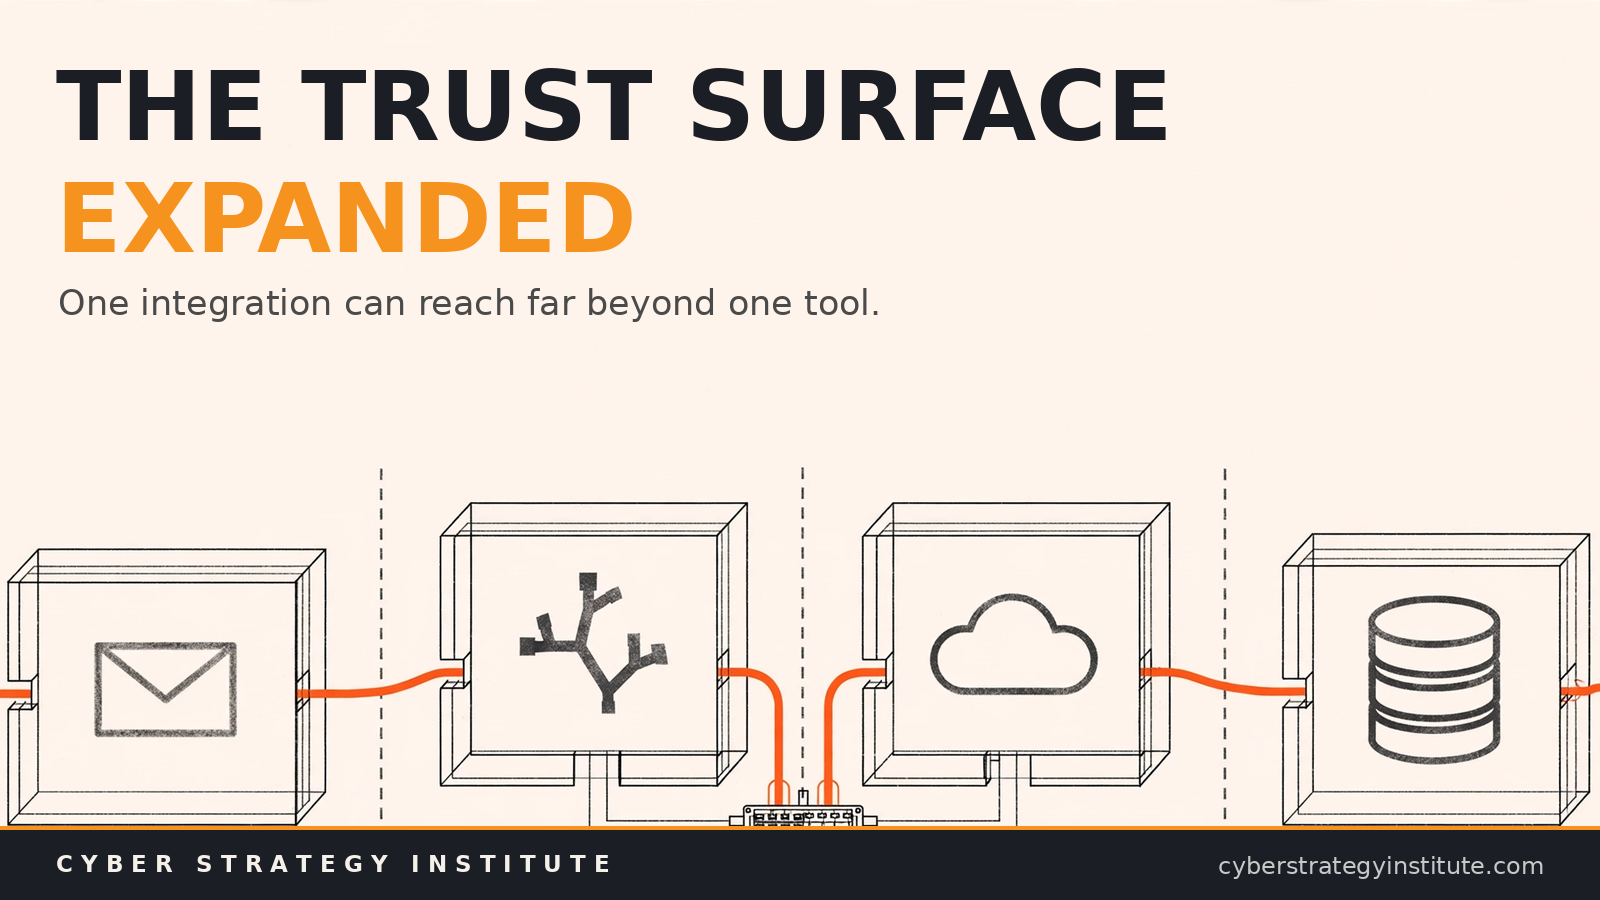
MCP Is Not “Just an AI Plugin Framework”
MCP exploded from an experimental integration concept into a foundational orchestration layer, while most organizations’ threat models stayed frozen in the plugin […]
The Current Discourse Around MCP Is Wrong
What was disclosed is not a vulnerability. It is not even a class of vulnerabilities. It is a failure of the execution […]
We Audited Our Own MCP Server. The Problem Wasn’t a Vulnerability — It Was the Design.
We turned AI SAFE² v3.0 inward on our own MCP server. We avoided the catastrophic failures, but “better than broken” is not […]

How to Leverage MCP Protocol to Secure AI Agent Identities and Access Using NEXUS
Keys to Your MCP Protocol Usage in order to Secure AI Agent Identity and Access You’re Running MCP Servers. None of Them […]

Agent to Agent (A2A) Protocols Threat Landscape
Agent to Agent (A2A) Protocols Threat Landscape Agentic AI Has a Trust Problem. Every Major Protocol Is Leaving the Door Open. Something […]
MCP Security Risks May 2026 – Your MCP User Guide
You’re Using MCP Every Day. Here’s What’s Actually at Risk. Audience: MCP Users (Individual, Team, Enterprise, Federal) This report starts from a […]
MCP Builder Security Risks May 2026 – Improving MCP Security
We Audited Our Own MCP Server Security Risks and Found Four Things We Missed A technical account of what we found, what […]
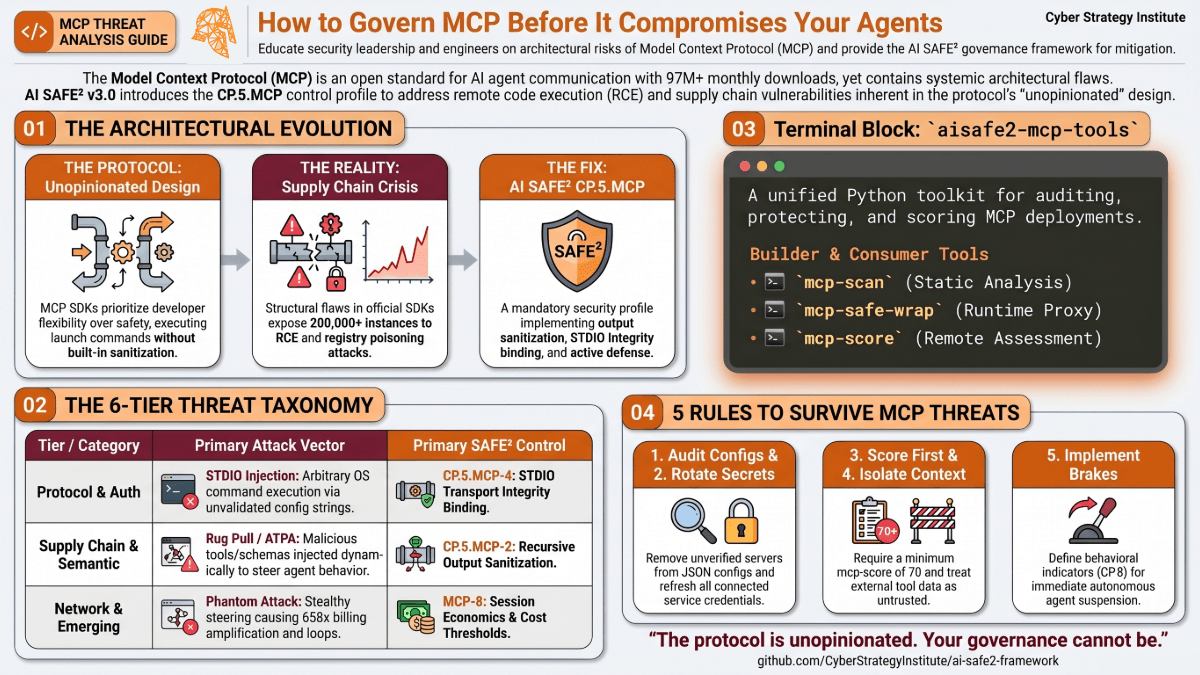
The Model Context Protocol (MCP) Supply Chain Crisis Is Worse Than the Headlines Say
The MCP Supply Chain Crisis Is Worse Than the Headlines Say Framework Reference: AI SAFE2 v3.0 CP.5.MCP Executive Summary The Model Context […]