Sovereign Engineering · Sovereign AI infrastructure
What Is Sovereign AI Infrastructure? The Architecture of Retained Authority
Sovereign AI infrastructure is an operating architecture that preserves an organization's required authority over AI deployment, data, identity, permissions, updates, evidence, and recovery. Location and model access matter. The deciding factor is whether the organization can exercise those rights when it needs them.
Intelligence can be rented; sovereignty must be owned. Ownership here means demonstrable decision rights and operating capability, including the ability to stop, replace, and recover the system.
By Cyber Strategy InstituteUpdated Framework source: AI SAFE² v3.1
Every layer has a named owner. The model is one replaceable component inside a persistent authority structure. Pick a dependency to remove and see the questions it raises.
- Does an approved alternate model path exist, and does it start disabled?
- Which protected actions stop until the replacement passes acceptance tests?
- Who authorizes the return to service?
- Does an approved local identity path exist, and how is revocation kept current?
- Can an operator still authenticate to stop the system?
- Which protected actions suspend when identity cannot be verified?
- How long can you safely run the current approved version?
- Who approves an out-of-band patch, and how is it verified?
- Can you roll back without the supplier?
01 · TL;DR
What does sovereign AI infrastructure actually require?
At a glance
TL;DR
- Data residency answers where information is processed or stored; sovereignty also asks who can authorize and control its use.
- Open weights and local compute are components of a sovereign design, not proof of the whole design.
- Test identity, policy, evidence, updates, recovery, and exit alongside inference.
- Hosted, hybrid, on-premises, and isolated deployments have different dependencies and operating burdens.
- Measure the workflows and decisions retained when a defined external service disappears.
- Core objective
- Retain the authority needed for the mission or business
- Strongest evidence
- Exercised administrative, authorization, continuity, and exit rights
- Common misunderstanding
- Local hardware means complete independence
- Human requirement
- A named owner who can inspect, challenge, redirect, and stop
- First step
- Map the authority required for one consequential workflow
A full sovereign stack — local control services for identity, policy, evidence, and recovery — is justified when the mission requires decisions to survive a defined external failure, and you can staff and maintain it. When the requirement is contractual authority and evidence access rather than continuity through a blackout, a hosted or hybrid design with documented rights to inspect, configure, revoke, replace, and export is the cheaper honest answer.
02 · Retained-authority matrix
Which rights can you exercise today?
For one consequential workflow, mark each right as Unknown, Documented, or Tested. Name the owner per row. Stays in your browser; download it as CSV.
| Component | Owner | Inspect | Configure | Revoke | Replace | Export |
|---|---|---|---|---|---|---|
| Identity | ||||||
| Policy | ||||||
| Data | ||||||
| Tools | ||||||
| Updates | ||||||
| Evidence | ||||||
| Recovery |
Unknown is a finding. Link the evidence for anything you mark Tested. There is no overall sovereignty score.
03 · The problem
The problem: the hardware is local, but the decision loop is elsewhere
A locally hosted model can still depend on a remote identity provider, policy service, license check, or update channel. If a required dependency disappears, you may retain the weights and lose the ability to operate the workflow.
The useful diagnostic is straightforward: which decisions can your organization still authorize and execute when the external hub is unavailable?
Infrastructure suppliers already provide private and disconnected deployment options.1 CSI's contribution is to connect the infrastructure choice to retained decision rights, explicit execution boundaries, and evidence the buyer can inspect. The architecture must show who controls the system, not merely where the GPUs sit.
04 · Architecture
How to build the sovereign stack
Use three architectural primitives.
- Retained administrative authorityIdentify who can inspect, configure, revoke, replace, and export each critical component.
- Operable local control services where requiredMatch identity, policy, evidence, and recovery dependencies to the continuity requirement.
- Exercised continuity and exitDemonstrate a useful, bounded operating mode when a defined dependency is removed.
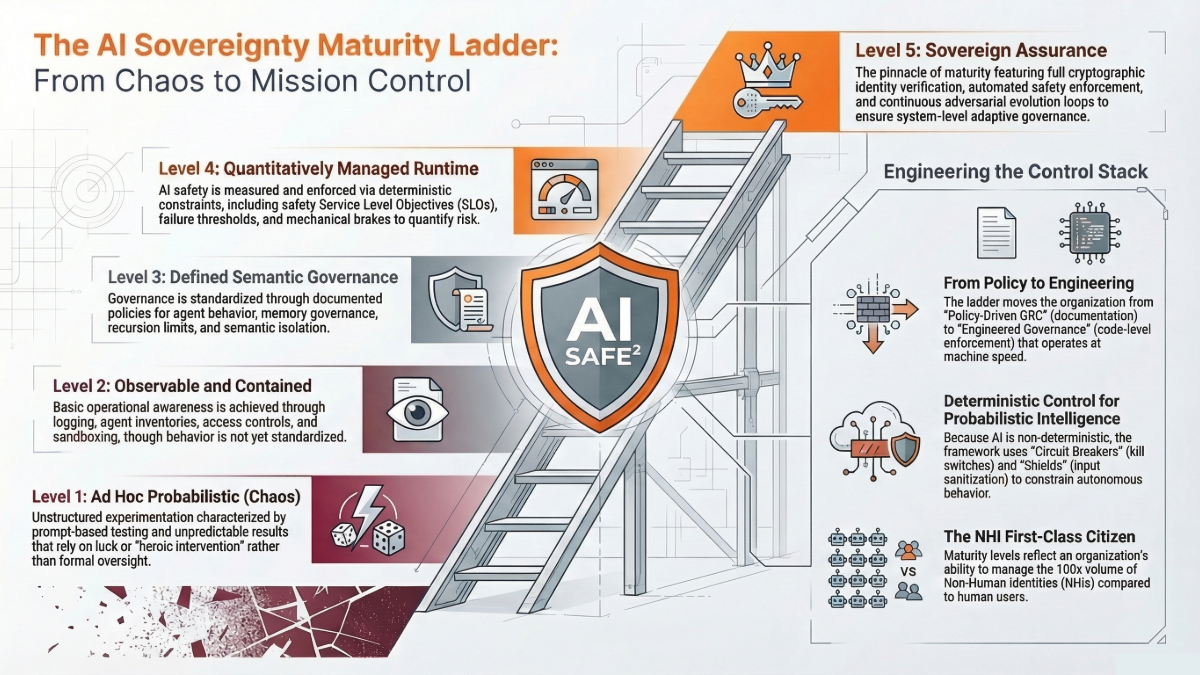
Open weights, AI SAFE² governance requirements, and local compute can form a strong starting stack. Complete it with licensed artifacts, maintained serving software, approved data, scoped tools, accountable operations, and tested recovery.
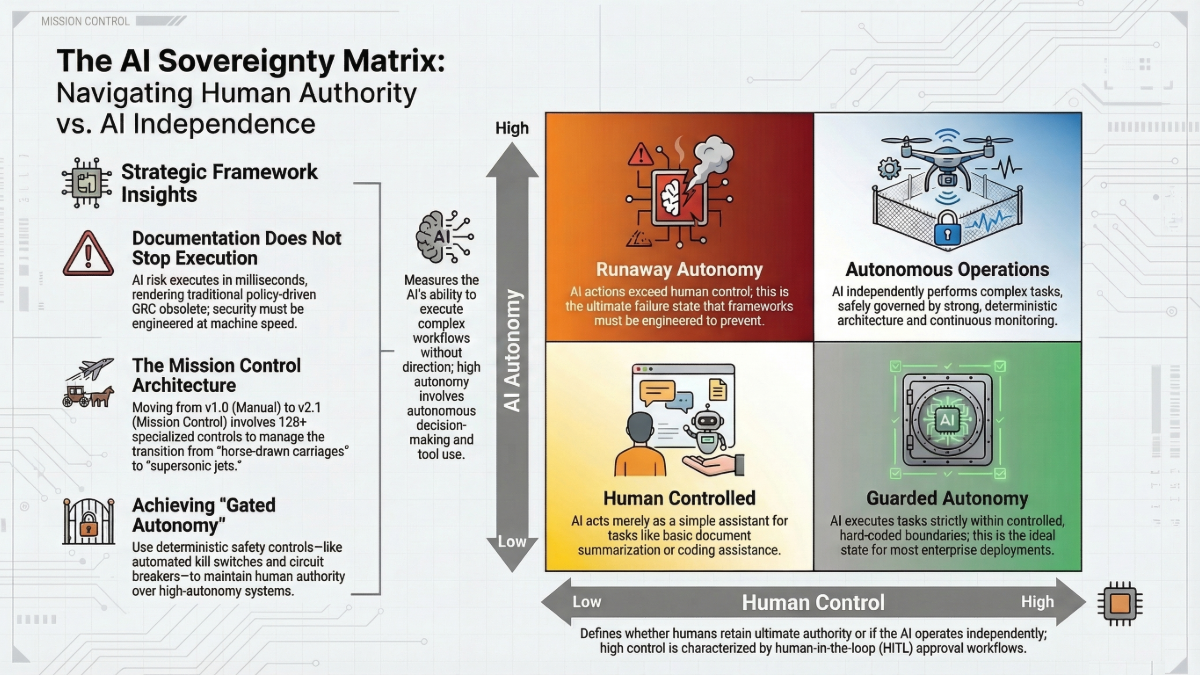
The “skull and brain” metaphor describes the relationship: the model provides capability; the surrounding architecture bounds what that capability may do. AI SAFE² supplies requirements. An implemented control plane enforces the relevant decisions. Keep those roles explicit.
# Illustrative retained-authority requirements, not executable policy.
workflow: internal-procurement-review
authority_owner: procurement-system-owner
required_rights: [inspect, configure, revoke, replace, export]
continuity:
  scenario: external-model-service-unavailable
  approved_mode: local-draft-only
  prohibited_actions: [purchase.submit, payment.release]
  exit_condition: owner-approved-restoration
evidence:
  location: customer-controlled-store
  includes: [authority_changes, decisions, tool_outcomes]
SOV-03 · Outage process
Preserve a decision loop when a dependency disappears
- Defined external service lost
- Check local authority services
- Required controls available?NoSuspend protected actions
- Select approved operating mode
- Action inside retained scope?NoSuspend protected actions
- Execute and retain evidence
- Reconcile after restoration
- Owner reviews recovery
05 · The governance gap
The governance gap: residency is one decision right
Ask who can change a policy, revoke an agent, recover evidence, replace the model, and authorize a return to service. A sovereignty claim becomes assessable when those rights are connected to an actual person, component, and procedure.
The Cognitive Sovereignty Framework adds the operator's capacity to understand and contest system recommendations.2 A nominal override is weak if its owner cannot see the consequence or reach the control during the failure scenario.
AISM organizational maturity and a technology's contribution are different assessments.3 A capable local deployment does not, by itself, establish the organization's maturity level.
Beside a consequential action, show
- Named role
- Procurement system owner
- Consequence
- Submits a purchase order to the supplier
- Granted scope
- Orders under the approved budget line
- Expiry
- End of the review cycle
- Source evidence
- Policy version and decision record
Illustrative layout. Educational mockup, no live approval control.
06 · Control mapping
AI SAFE² control mapping
Use these controls to structure an architecture review, with applicability and evidence recorded separately.4567
| Published control | Sovereignty question | Evidence to request |
|---|---|---|
| CP.3ACT Capability Tiers 1–4 | What level of autonomy does the actual deployment exercise? | Scoped capability classification |
| CP.4Agentic Control Plane Governance | Who owns identities, grants, orchestration, and revocation? | Authority map and administrator roles |
| CP.8Catastrophic Risk Threshold Controls | Which conditions require suspension? | Stop thresholds and observed decisions |
| CP.10HEAR Doctrine | Who can halt the governed deployment where required? | Named assignment and usable halt path |
| A2.4Dynamic Agent State Inventory | Can you account for active agents and permissions? | Current reconciled inventory |
| F3.5Multi-Agent Cascade Containment | Can one failed dependency destabilize the workflow? | Dependency-failure and recovery exercise |
| E5.1Continuous Adversarial Evaluation Cadence | Are changed models and tools reevaluated? | Change-triggered test records |
HEAR: Human Ethical Agent of Record · ACT: CSI's agent capability tiers
07 · Compare
Compare infrastructure choices
| Architecture | Potential advantage | Dependency or operating burden | Required question |
|---|---|---|---|
| Hosted model API | Managed model operation and access to provider capabilities | Provider availability, terms, supported controls | Can required authority and evidence survive provider loss? |
| Private cloud | Dedicated configuration and deployment options | Cloud administration, region, service dependencies | Who can operate and recover the control services? |
| On-premises | Direct control of local infrastructure | Capacity, patching, hardware, staffing | Can the organization actually maintain it? |
| Air-gapped | Defined separation from external networks | Import, updates, local dependencies, transfer discipline | Can the full workflow operate inside the boundary? |
None of these labels resolves legal jurisdiction, contractual rights, or sector-specific obligations by itself. Evaluate those requirements with the appropriate owners.
08 · Test your claim
Test your claim: remove a defined dependency
- Choose one external service and a required operating duration before the exercise.
- Document the useful work that must remain available and the actions that must stop.
- Disable the dependency in staging.
- Verify authentication, permissions, model access, tool restrictions, evidence creation, revocation, and recovery.
- Record retained workflows and unavailable functions separately.
Fail the claim if
Fail the claimed continuity scope if a required workflow cannot complete under its stated controls. Fail the authority claim if permissions silently broaden or stopping authority no longer works. The proposed test produces evidence for that scenario only, not a universal sovereignty certificate.
This is a test you can run against your deployment. No CSI result is reported here. Record the versions, permitted scope, observed actions, failures, and legitimate task completion before drawing a conclusion.
09 · FAQ
Frequently asked questions about sovereign AI infrastructure
What is sovereign AI infrastructure?
It is infrastructure and operations designed to preserve specified authority over AI systems, including permissions, data, deployment, updates, evidence, and recovery.
Is sovereign AI the same as data residency?
No. Residency concerns location. Sovereignty also concerns decision rights, operational dependencies, and the ability to exercise control.
Must sovereign AI use open weights?
Open weights can improve deployment options. Define the required rights, licenses, dependencies, and continuity scope before selecting a model arrangement.
Can cloud infrastructure support a sovereign design?
It can support specified sovereignty objectives. Evaluate administration, legal exposure, dependencies, evidence access, and exit rights against the actual requirement.
Does a local control plane eliminate every dependency?
No. It changes where decisions are enforced. Hardware, updates, identity, keys, and staff remain dependencies to document and test.
Does an AI SAFE² mapping establish an AISM maturity level?
No. A mapping identifies relevant controls. Organizational maturity requires its own scoped assessment and evidence.3
10 · Next steps
What to do next
- Define the mission and authority that must survive disruption.
- Map the people and services required to exercise that authority.
- Compare deployment options against those requirements.
- Exercise one external dependency loss and recovery.
- Publish the retained scope internally, including what must stop.
The challengeWhen the external hub goes dark, which decisions can your organization still authorize and execute?
Start with the authority you need to retain
Establish your governance baseline, then use it to guide a scoped infrastructure and continuity review.
11 · Sources and method
Sources and method
Sources
- Red Hat, OpenShift AI Self-Managed documentation. Disconnected deployment guidance; not a sovereign outcome guarantee.
- Cyber Strategy Institute, Cognitive Sovereignty Framework. Framework doctrine, not independently established outcome claims.
- Cyber Strategy Institute, AI SAFE² framework README, pinned source. Publisher documentation, not independent efficacy evidence.
- Cyber Strategy Institute, Cross-Pillar Governance Layer, pinned source. Requirements and reference patterns, not evidence of installed coverage.
- Cyber Strategy Institute, Pillar 2, Audit & Inventory, pinned source. A listed trace requirement does not prove access to private model reasoning.
- Cyber Strategy Institute, Pillar 3, Fail-Safe & Recovery, pinned source. Behavior and containment need deployment-specific tests.
- Cyber Strategy Institute, Pillar 5, Evolve & Educate, pinned source. Evaluation requirement, not a reported pass.
Method
Sources reviewed . AI SAFE² is cited from its October 15, 2026 release. Framework documents identify v3.1; the NEXUS README identifies v0.6.0. These version numbers describe different artifacts. Control mappings are editorial applicability mappings, not conformance determinations. Every CSI exercise on this page is a proposed test; no CSI result is reported.
Update log
- : page published.
About
Published by Cyber Strategy Institute, author of the AI SAFE² framework.